Problem Introduction
AWS IAM access keys provide programmatic access to cloud resources for applications, automation scripts, and users. Over time, these long-lived credentials can become dormant or remain active long after they are no longer required. Unrotated or forgotten access keys represent a major security risk if compromised, an attacker can exploit them to gain unauthorized access to AWS infrastructure. Manually reviewing IAM users and key activity across an organization is time-consuming and prone to human error, resulting in a lack of continuous visibility into active, unused, and stale credentials.
How GRiPO Helps You in This Situation
GRiPO transforms manual cloud credential audits into an automated monitoring pipeline. Instead of requiring engineers to manually inspect IAM accounts, GRiPO periodically collects IAM telemetry and evaluates access key activity against rotation policies. The workflow identifies active, inactive, never-used, and stale keys, calculates risk severity, and dispatches automated alerts so security teams can revoke unnecessary credentials before they cause a breach.
GRiPO Solution
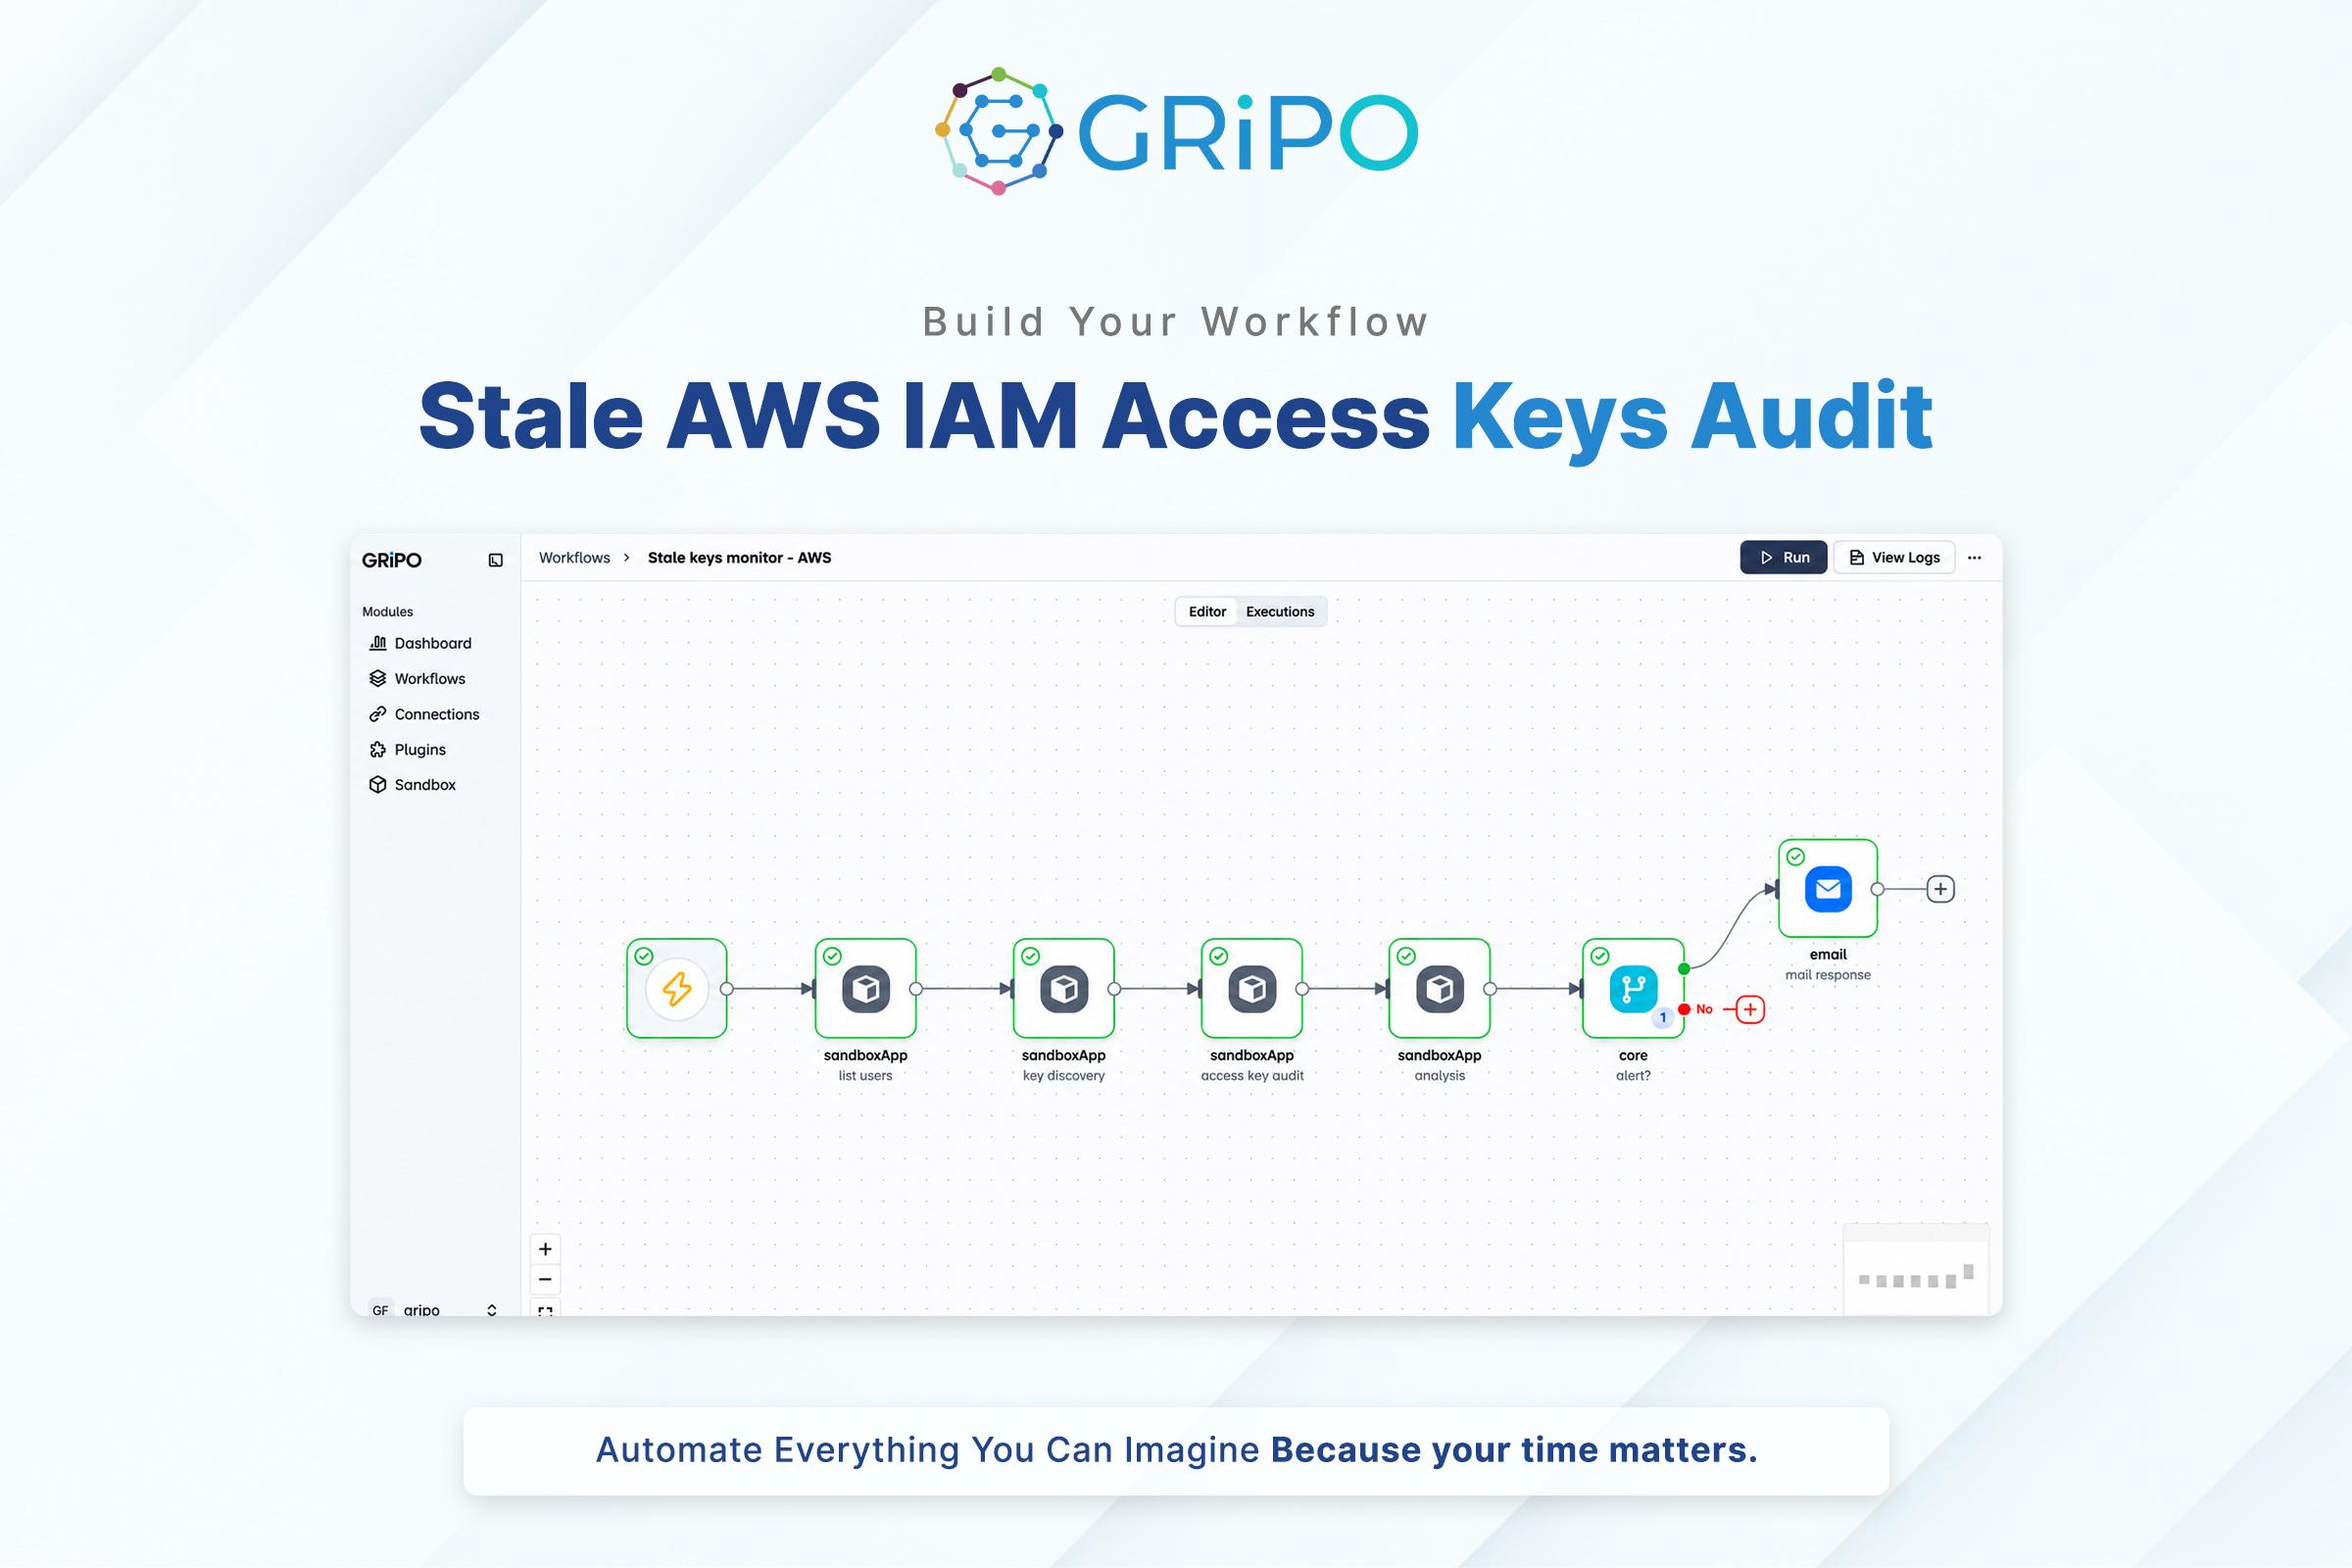
The Stale AWS IAM Access Key Audit uses a secure AWS connection with read-only IAM permissions (iam:ListUsers, iam:ListAccessKeys, iam:GetAccessKeyLastUsed) to analyze credential health without requiring local AWS CLI installations. Operating via a weekly scheduled trigger, Node A1 discovers IAM users, Node A2 collects access key telemetry, Node A3/A4 performs risk analysis against defined age thresholds (e.g., keys older than 90 days), and the final alert node notifies the security team when intervention is required.
| Finding Classification | Condition / Criteria | Risk Severity | Workflow Action |
| Stale Active Key | Key is active and older than 90 days. | HIGH | High-priority alert sent; immediate review required. |
| Never Used / Aging Key | Key exists but has never been used or is approaching 90 days. | MEDIUM | Standard alert sent; rotation/deletion recommended. |
| Active & Compliant | Key is active, recently rotated, and regularly used. | LOW | Logged as compliant; no alert required. |
Automated Stale AWS IAM Access Key Audit
The workflow automates cloud hygiene by executing on a weekly schedule. It aggregates IAM metadata, checks last-used service metrics, flags keys violating the 90-day rotation policy, and dispatches an itemized email report to security owners. This eliminates permanent backdoor risks without introducing complex management infrastructure.