Problem Introduction
AWS security groups control the inbound and outbound traffic allowed to cloud resources. Rules that are too permissive or expose services unnecessarily can create security risks. Security teams need to review the rules, identify services exposed to the internet, and check the associated network interfaces and public IP addresses. Doing this manually takes time and makes it harder to identify risks and prioritize issues.
How GRiPO Helps You in This Situation
The challenge isn’t having different tools, it’s getting them to work together. When the output of one system has to feed another for analysis, action, or AI insights, teams end up moving data manually, maintaining custom scripts, or building complex ETL pipelines. GRiPO Flow connects these tools into a single workflow where data, insights, AI analysis, and actions flow between systems automatically, reducing manual effort.
GRiPO Solution
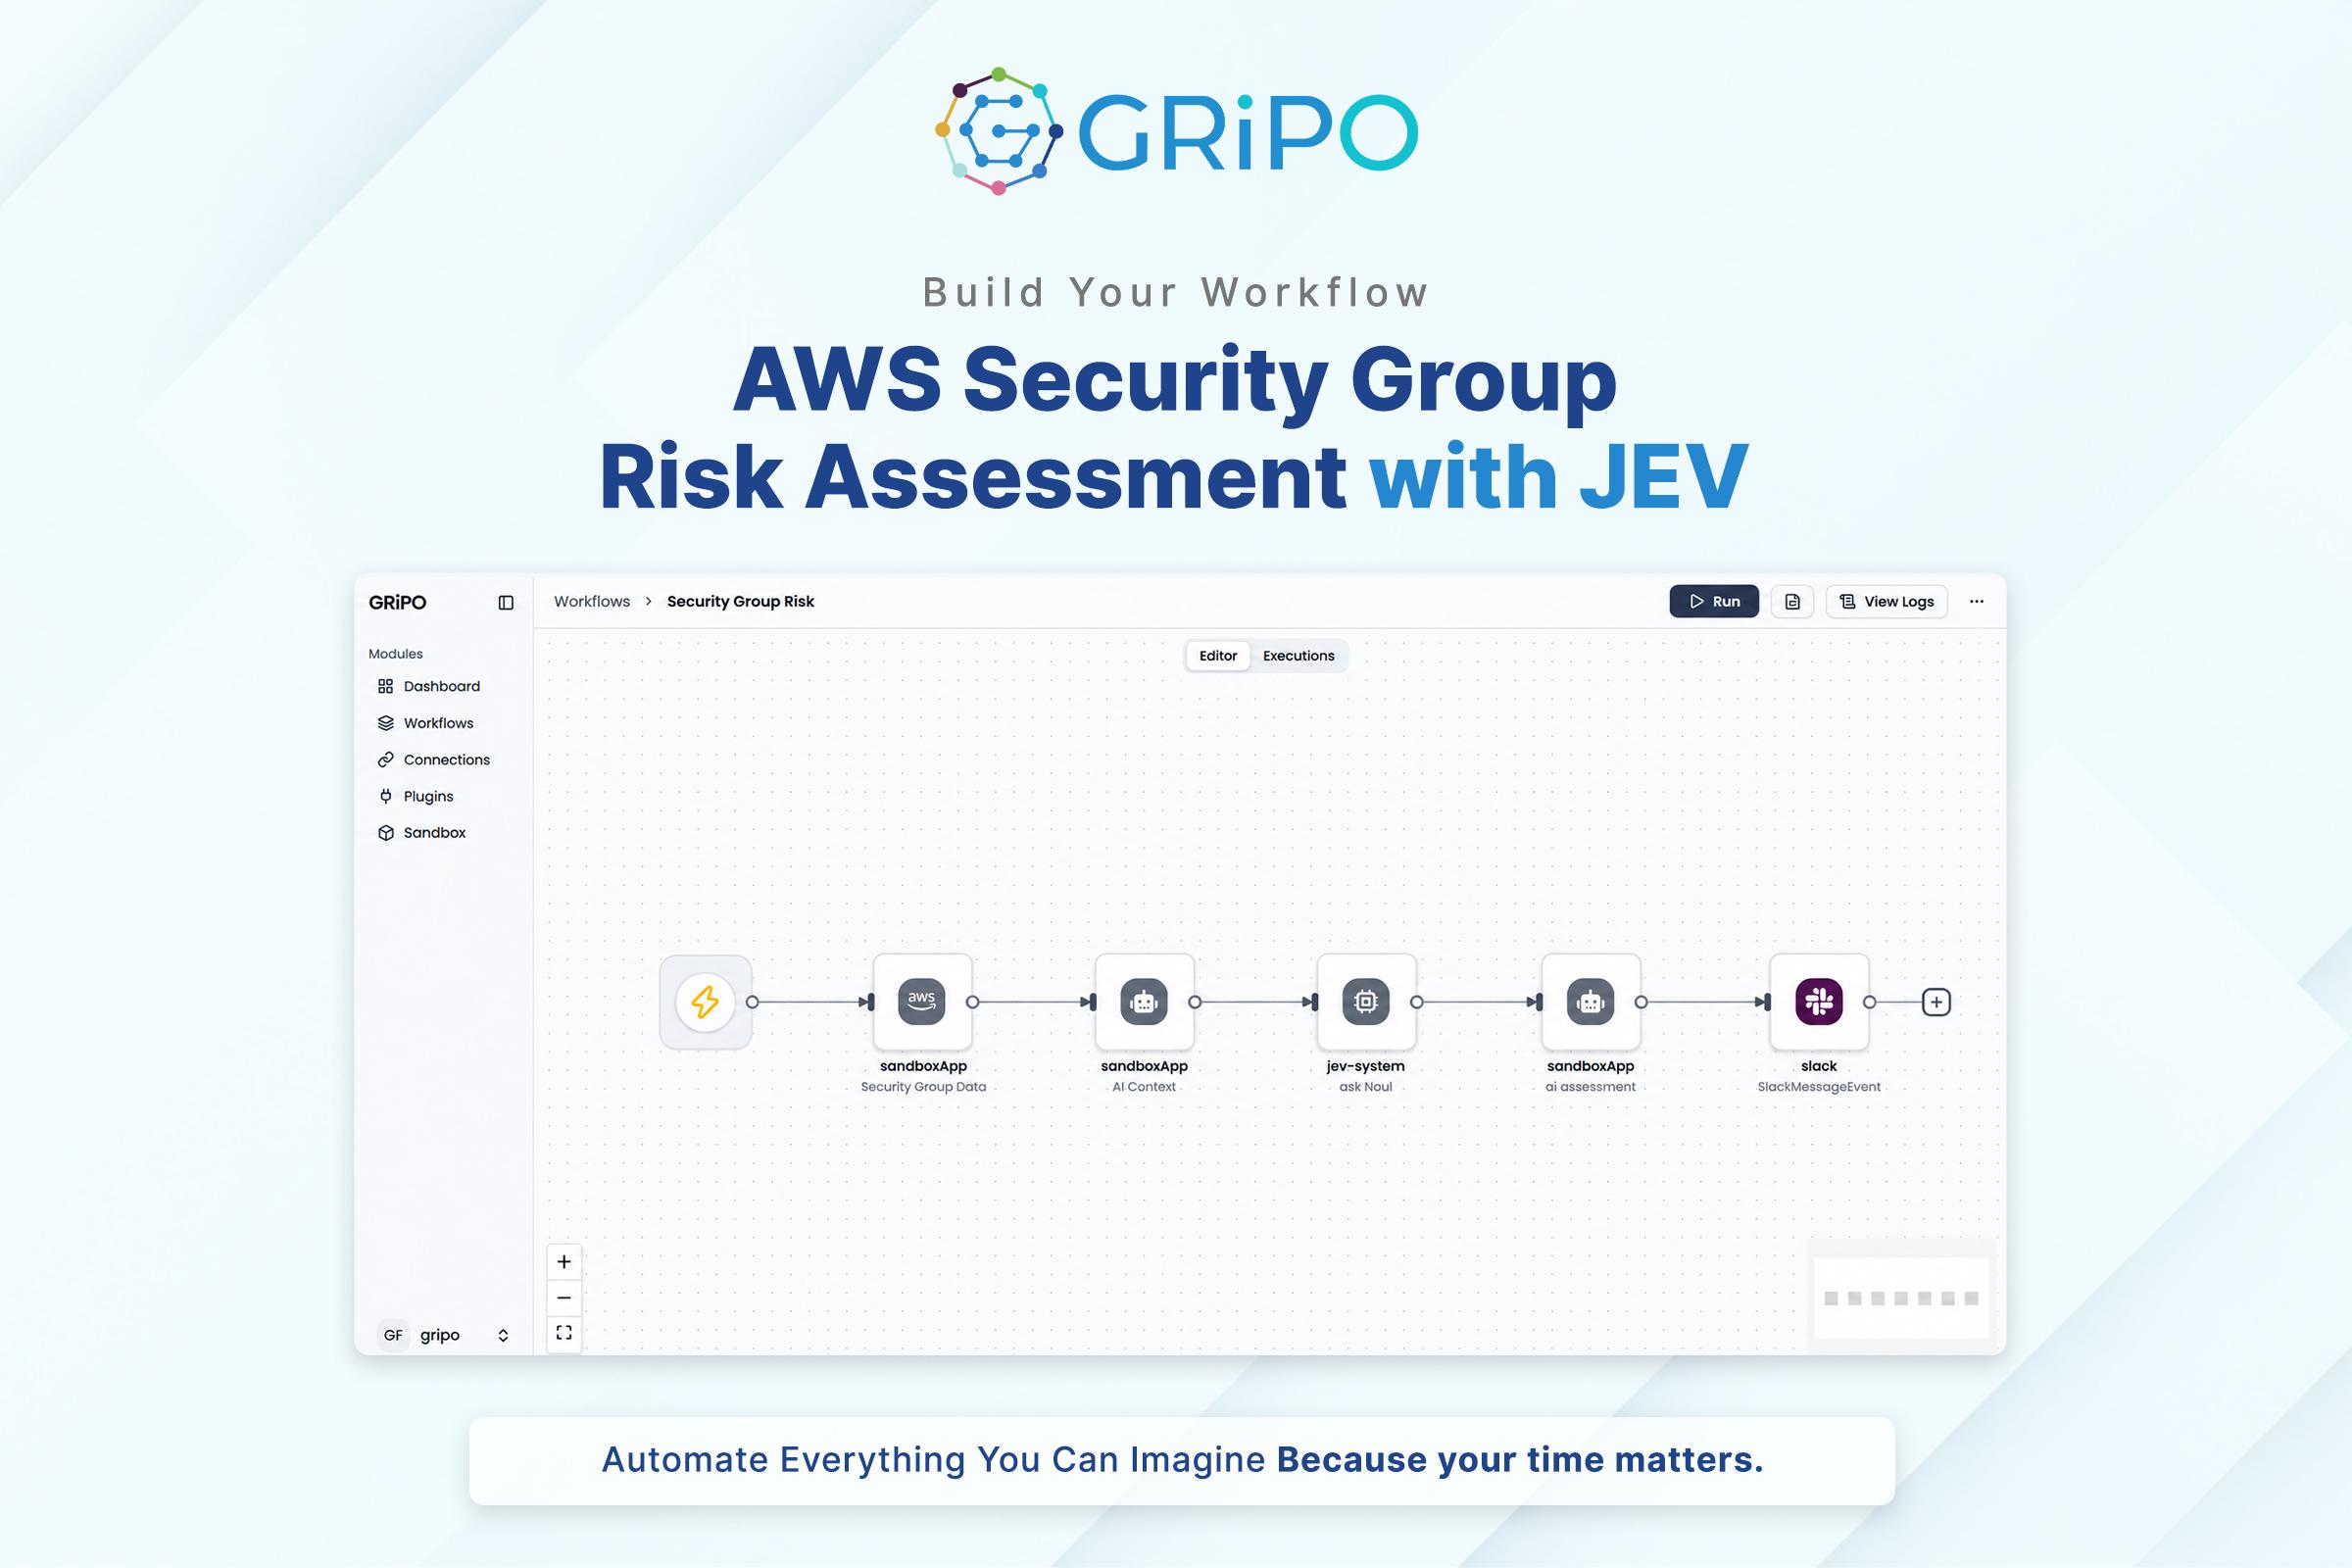
jev is a System One model designed to make fast, structured decisions. Instead of generating text, it returns a defined decision that can be used directly for routing and automated actions. GRiPO supports jev as a plugin. In this workflow:
- On-Demand Trigger: runs the assessment whenever the team needs to review security group configurations.
- Security Group Data: retrieves data using the security group ID and region, including inbound and outbound rules, rules open to the world, attached network interfaces, and public IP information.
- AI Context: organizes the data into a structured context for jev.
- jev Noul: evaluates the context and instructions and returns a structured decision. It does not generate the full report. The decision is passed to the Gemini Assessment activity.
- AI Assessment: Gemini uses the security group data and jev’s decision to generate an assessment with the available risk score, key findings, missing evidence, and areas requiring analyst attention.
- Slack Message Event: sends the assessment to the configured Slack channel.
Automated AWS Security Group Risk Assessment
The workflow runs on demand. It retrieves security group data, prepares the AI context, passes it to jev for a structured decision, generates a Gemini assessment, and sends it to Slack. In the example run, the report shows a risk score of 0.41, inbound SSH restricted to a specific IP address, and outbound traffic allowed to all destinations. It recommends reviewing whether unrestricted outbound access is necessary for the attached EC2 instance.