Problem Introduction
Assessing an AWS IAM access key means reviewing its status, creation timestamp, and last-used details (date, service, region). Pulling this evidence from AWS manually and deciding how much security concern it represents is time-consuming. It is also easy to do inconsistently, especially when some evidence is missing.
How GRiPO Helps You in This Situation
The challenge isn’t having different tools, it’s getting them to work together. When the output of one system has to feed another for analysis, action, or AI insights, teams end up moving data manually, maintaining custom scripts, or building complex ETL pipelines. GRiPO Flow connects these tools into a single workflow where data, insights, AI analysis, and actions flow between systems automatically.
GRiPO Solution
jev is a System One model designed to make fast, structured decisions. Instead of generating text, it returns a defined decision. GRiPO supports jev as a plugin. In this workflow:
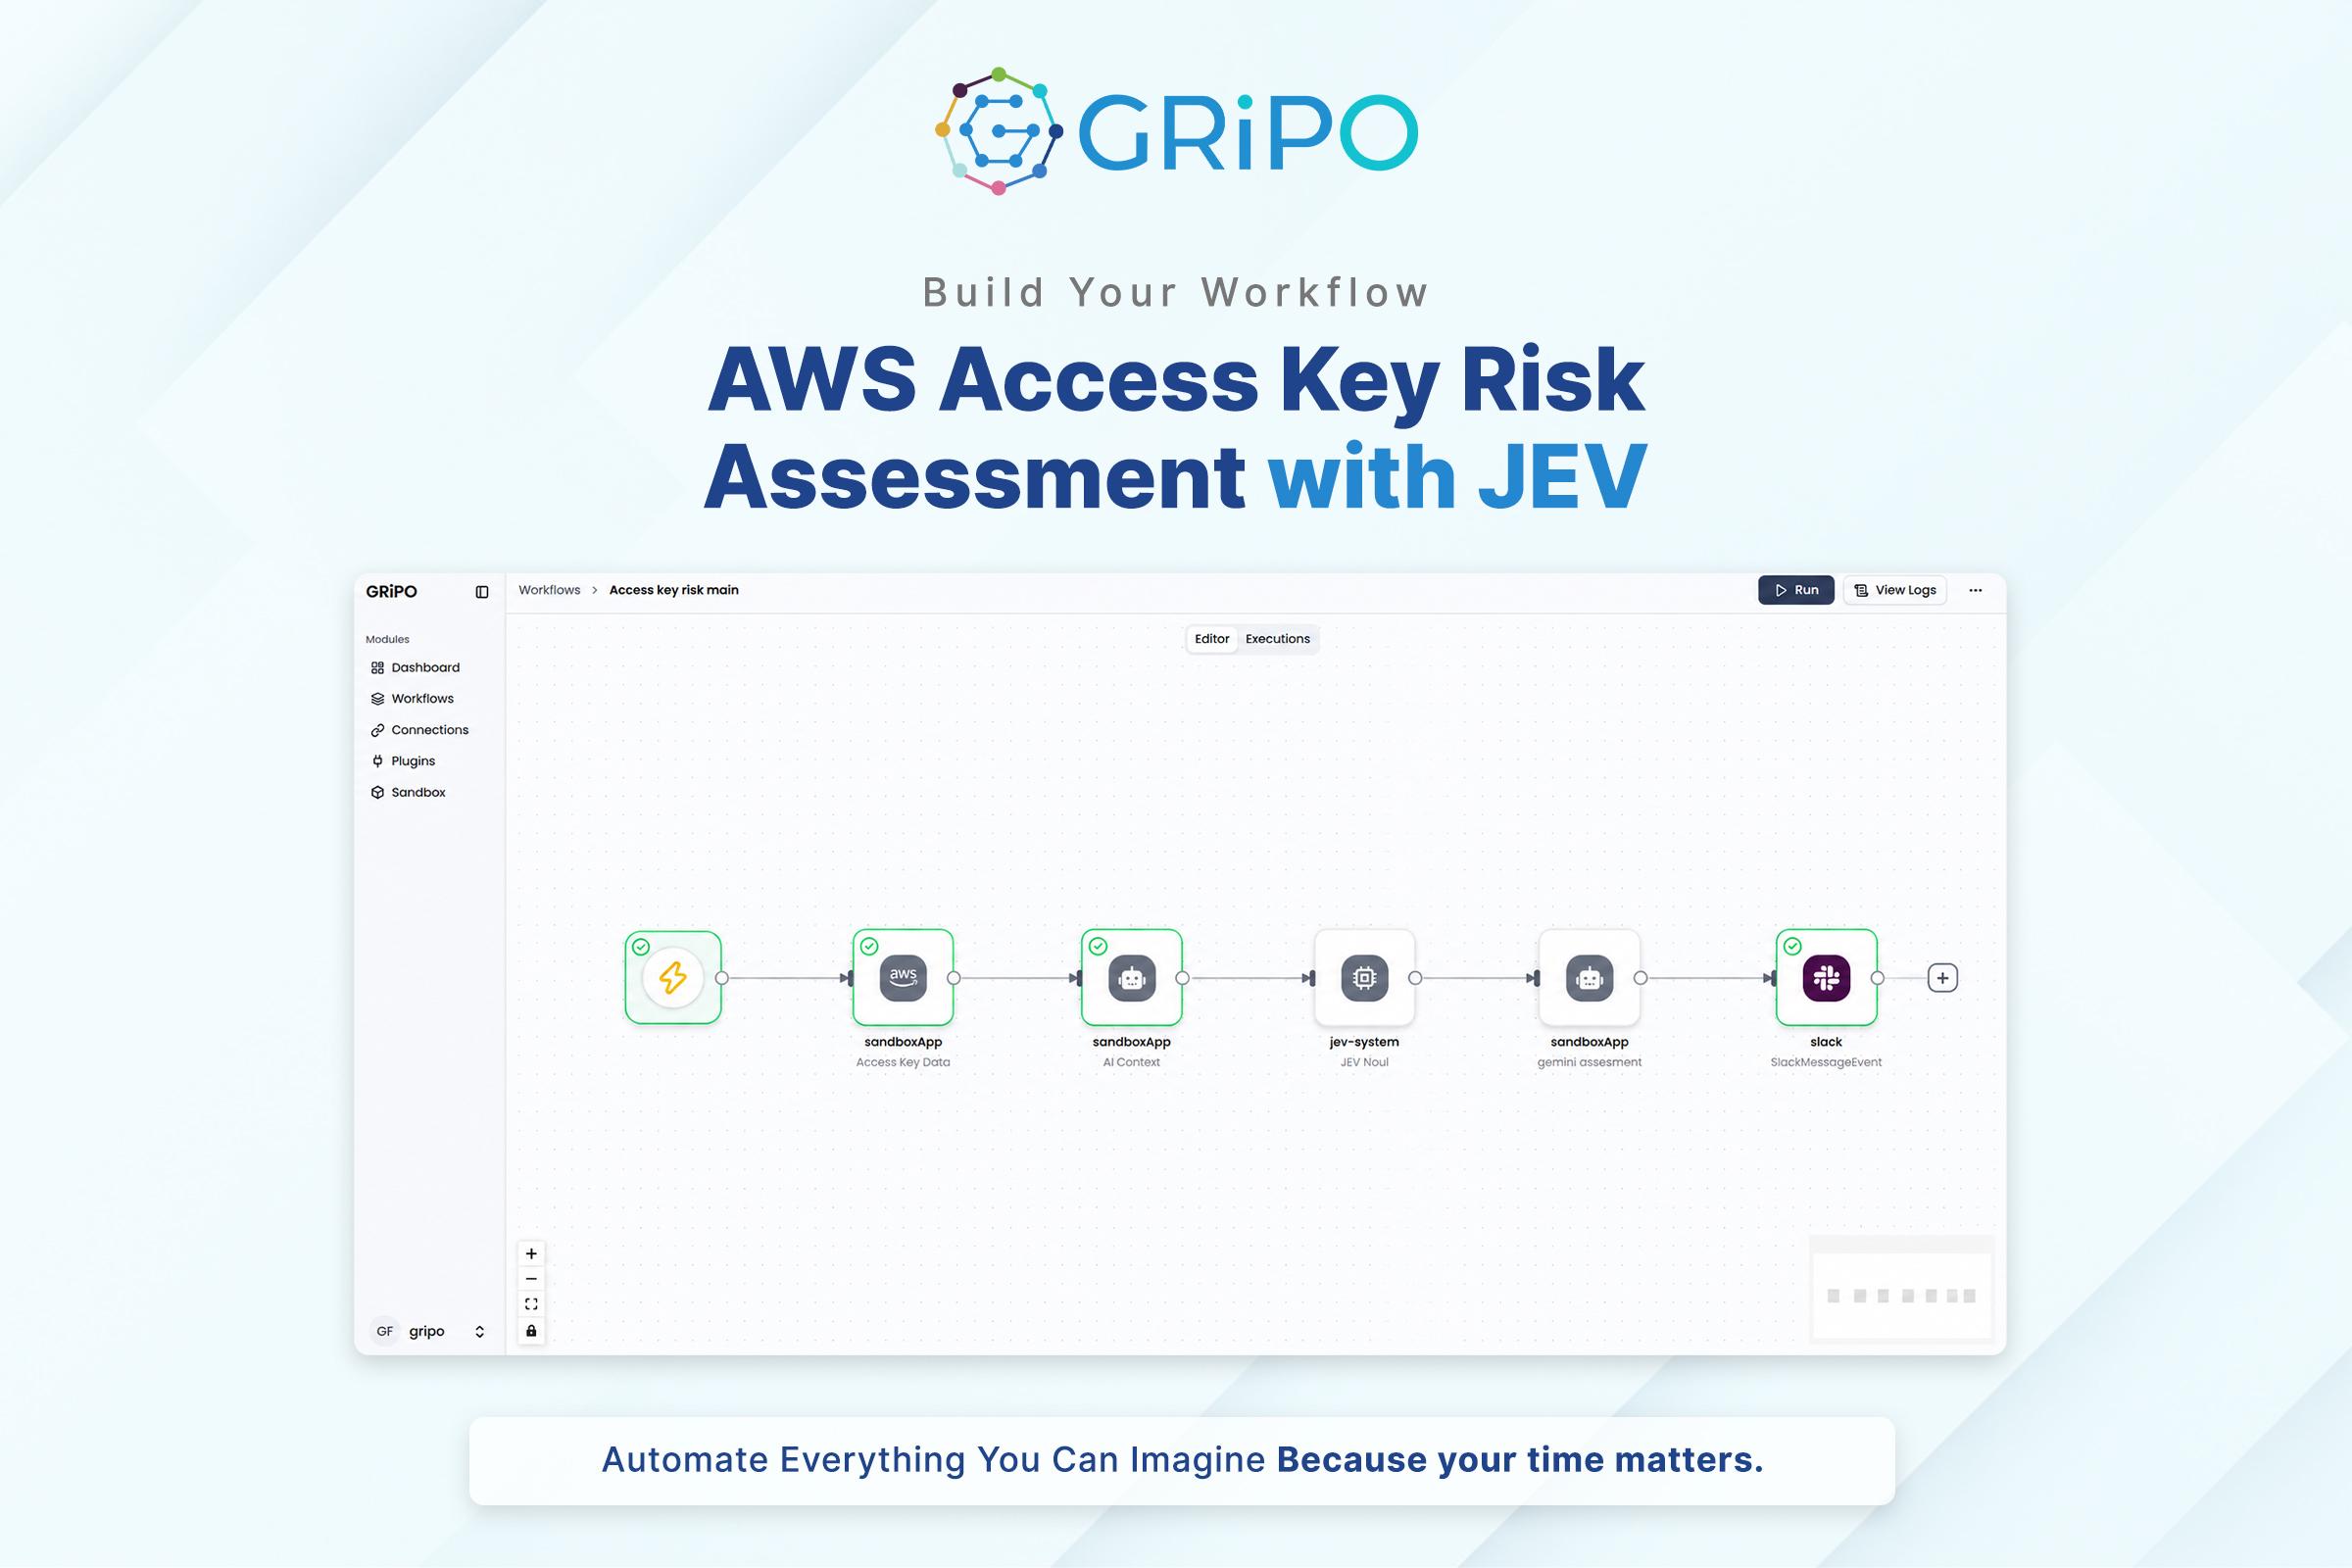
- On-Demand Trigger: runs with two inputs, the IAM username and the access key ID.
- Access Key Data: runs AWS CLI commands in a sandbox (list-access-keys and get-access-key-last-used). It returns the key’s status, creation date, last-used date, service, and region. If listing fails or the key isn’t found, it returns an error status.
- AI Context: Gemini organizes the data into a structured JSON context: identity, access key, usage, observations, and investigation context including missing information. It is instructed not to calculate risk, assign severity, judge compromise, or recommend remediation.
- JEV Noul: jev returns a risk score from 0 (minimal concern) to 1 (severe concern). It evaluates only the supplied evidence and is told not to assume that an old key, recent usage, a particular service, or a particular region means compromise.
- Gemini Assessment: Gemini treats jev’s result as authoritative and does not create a different score. It returns a structured report: risk score, assessment, key findings, missing evidence, and analyst attention.
- Slack Message Event: posts the assessment to the configured Slack channel.
Automated AWS Access Key Risk Assessment
The workflow runs on demand for a given IAM user and access key. It collects the key’s status, creation, and last-used data from AWS, prepares a structured context, and has jev return a 0–1 risk score. Gemini then explains that score from the evidence, and the report is posted to Slack with key findings, missing evidence, and analyst-attention points.