Problem Introduction
Developers may accidentally commit sensitive credentials such as API keys, access tokens, cloud passwords, and private keys into GitHub repositories during feature development. Relying solely on manual code reviews is prone to human error, while full-repository history scans produce excessive false positives by flagging legacy secrets not introduced by the current Pull Request (PR). Teams require an automated PR-level gate that isolates and analyzes only newly introduced code changes, reports findings directly to GitHub, blocks compromised PRs from passing validation, and sends automated security notifications.
How GRiPO Helps You in This Situation
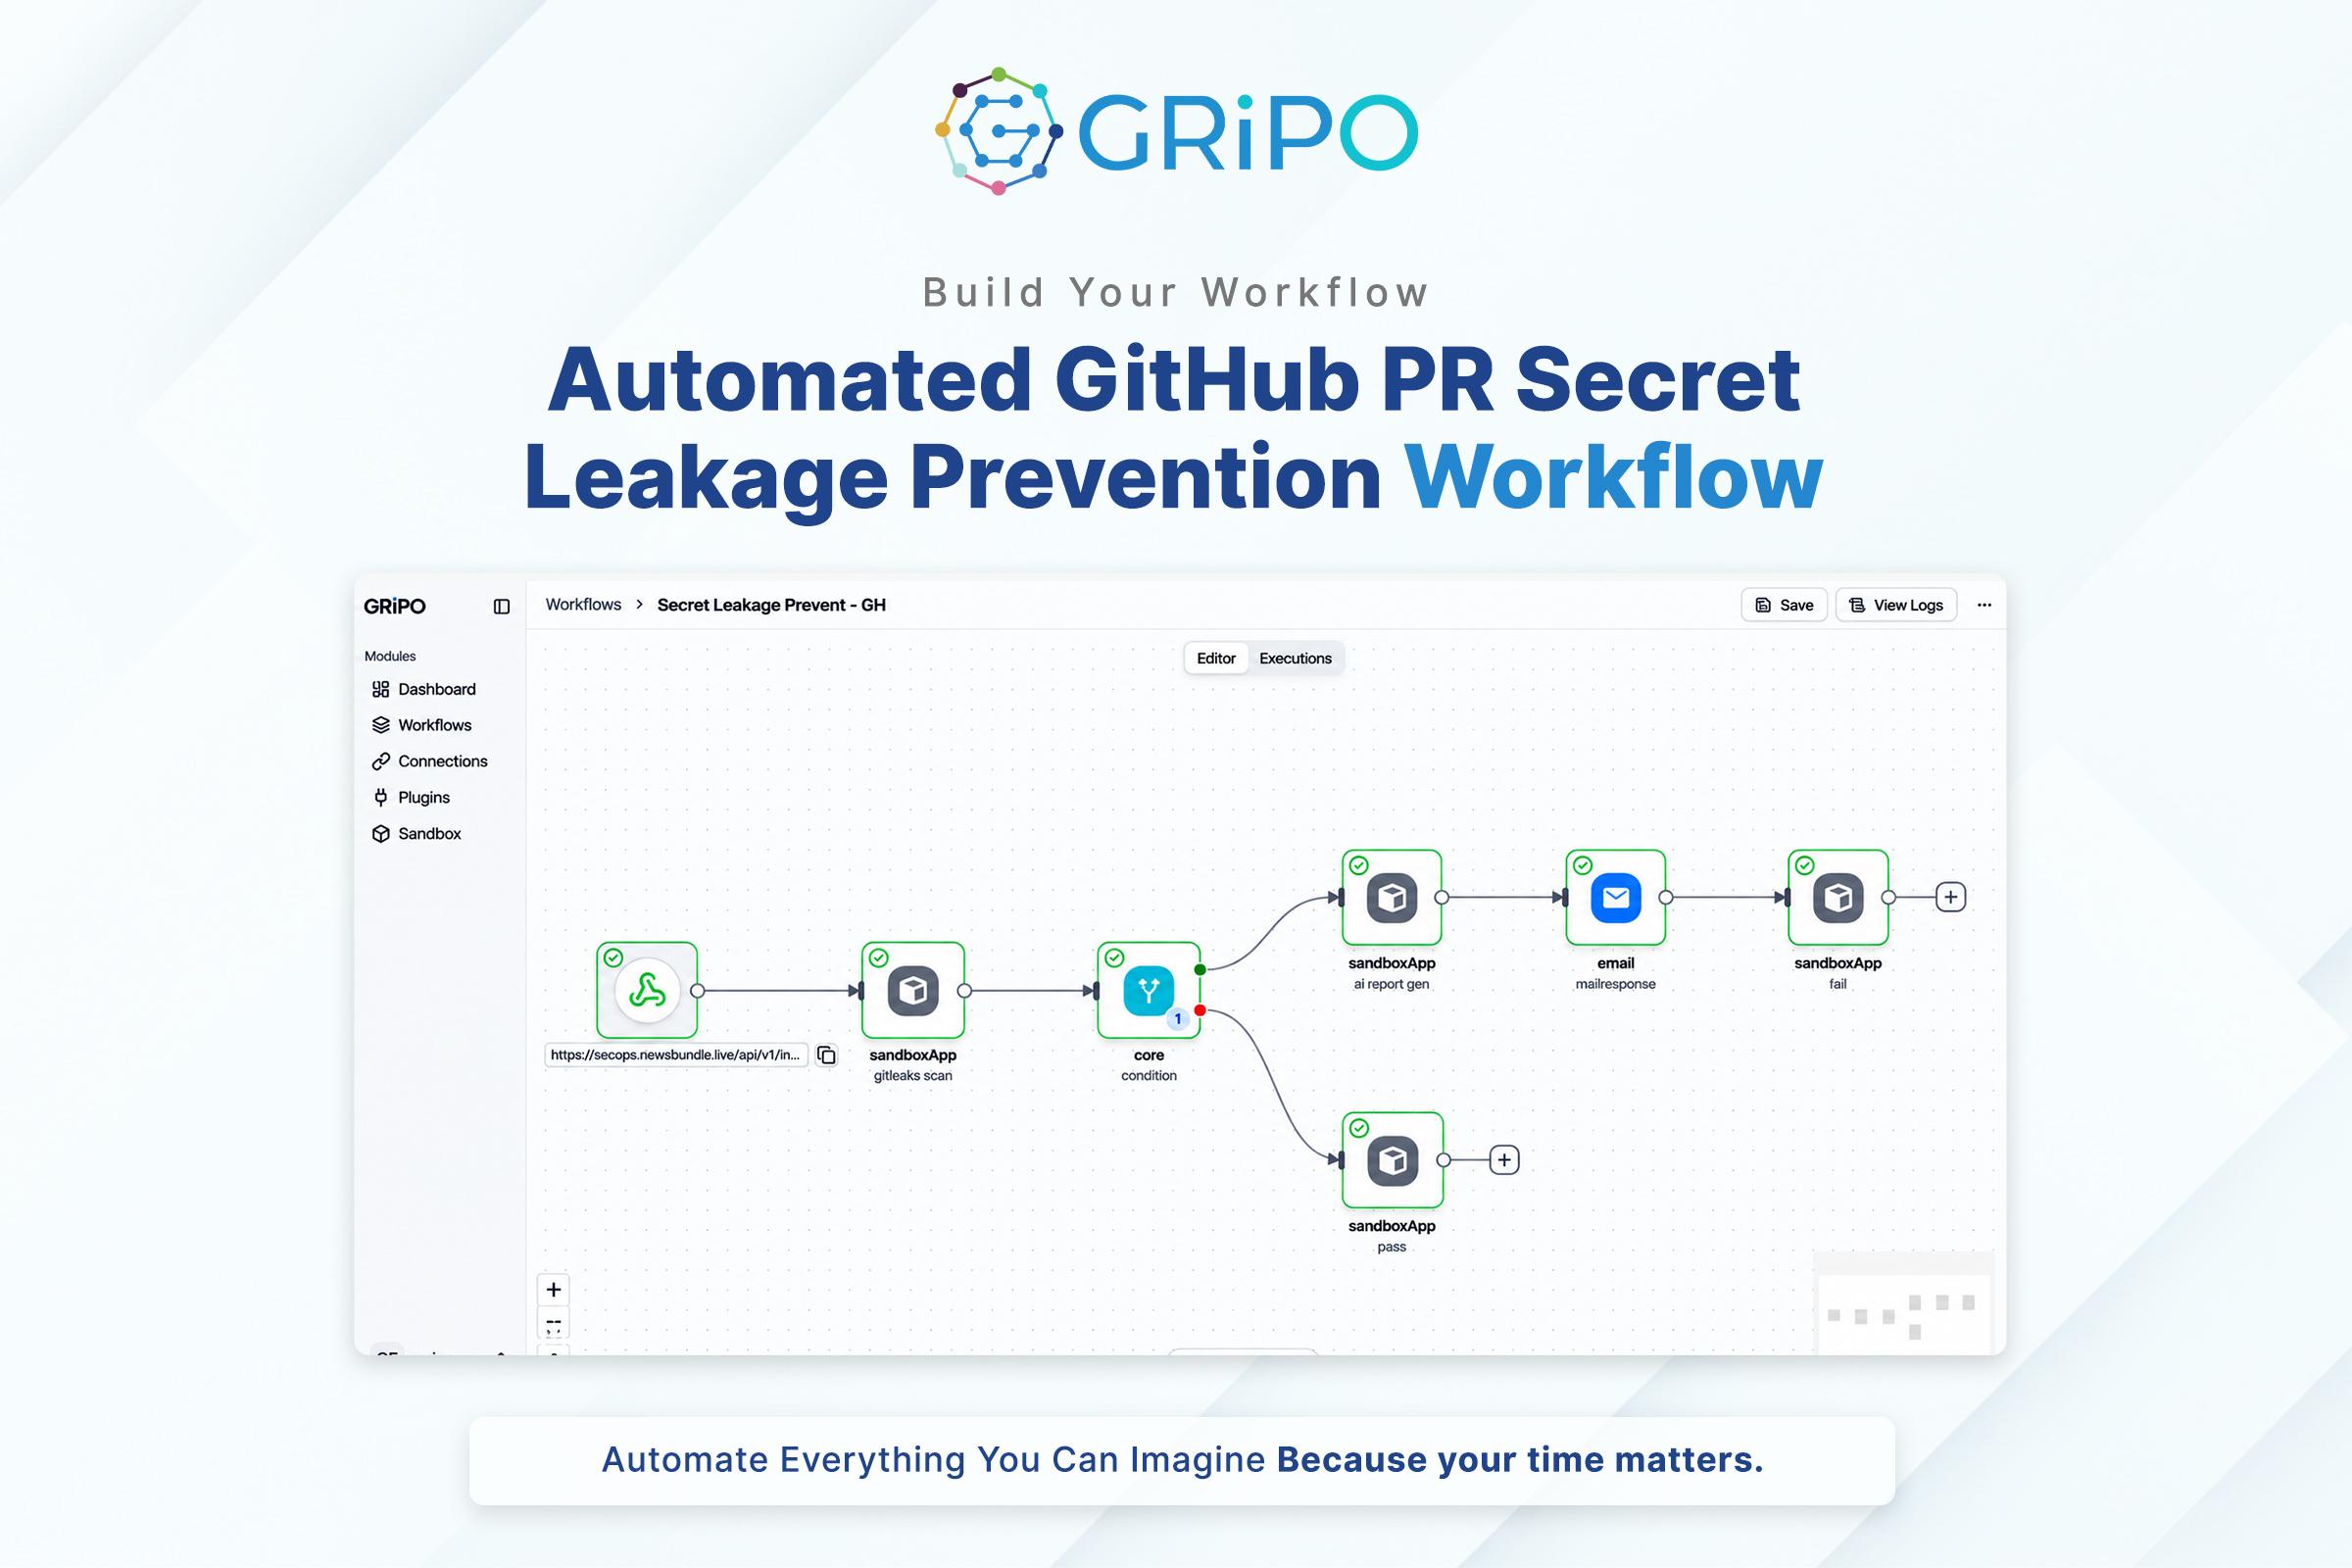
GRiPO automates PR secret detection by integrating directly with GitHub webhooks and GitHub Actions. Upon PR events (opened, synchronize, reopened), GitHub transmits key metadata including repository details, base branch, and exact HEAD commit SHA—to GRiPO. Rather than scanning historical commits, GRiPO executes a targeted Gitleaks scan against only the added lines in the current PR diff. It then updates the GitHub commit status to dynamically block or permit PR progress.
GRiPO Solution
The solution establishes a synchronous security gate using GRiPO and Gitleaks. When a PR is created or updated, GitHub Actions notifies GRiPO, which retrieves the diff, extracts added changes, and runs Gitleaks pattern matching. The resulting evaluation updates the commit status for the precise HEAD SHA, ensuring old repository history is ignored while newly introduced secrets trigger a failure.
| Scan Output Status | Condition / Findings | Commit Status State | Workflow & PR Outcome |
| SUCCESS | 0 secrets detected in newly added PR changes. | success | Action exits code 0; PR security check passes. |
| FAILURE | 1+ secrets detected (e.g., AWS, Slack, Stripe, Private Keys). | failure | Action exits code 1; PR security check fails & blocks merge. |
| ERROR | Scanner execution failure or error encountered. | failure | Action flags error; PR check blocked until resolved. |
Automated GitHub PR Secret Leakage Prevention Gate
The workflow continuously intercepts PR activity. By targeting the exact HEAD_SHA and inspecting diff additions, Gitleaks flags compromised credentials (such as Slack tokens, cloud credentials, or database keys). A polling wait loop in GitHub Actions ensures the PR build fails synchronously if secrets are discovered, giving developers immediate remediation feedback.